Claude Security now continuously monitors connected repositories as code changes, tracks vulnerabilities through remediation, and uses team-supplied context to decide which risks matter most. The updated service is available in public beta for Claude Enterprise customers, eliminating the need to start each scan manually.
Claude Security now keeps up with your code as it changes.
— Claude (@claudeai) October 21, 2026
Connect your repositories once. Claude runs a deep first scan, then re-scans as changes land, so findings stay close to the current state of your code.
In public beta on Claude Enterprise. pic.twitter.com/J5kPSEhWp3
Organizations create a project, connect repositories through the Claude GitHub app, including GitHub Enterprise Server, or use access tokens for GitLab and other Git providers. After teams choose the relevant branches and scope, Claude runs a deep baseline scan and regularly checks new changes according to their risk and complexity. Projects can include multiple repositories, allowing the system to catch weaknesses that cross service boundaries, such as a backend trusting input that a client was expected to validate.
Claude Security checks open findings against changed code and marks them fixed when the correction lands, including fixes completed outside Claude Code. A finding automatically reopens if the vulnerability appears again.
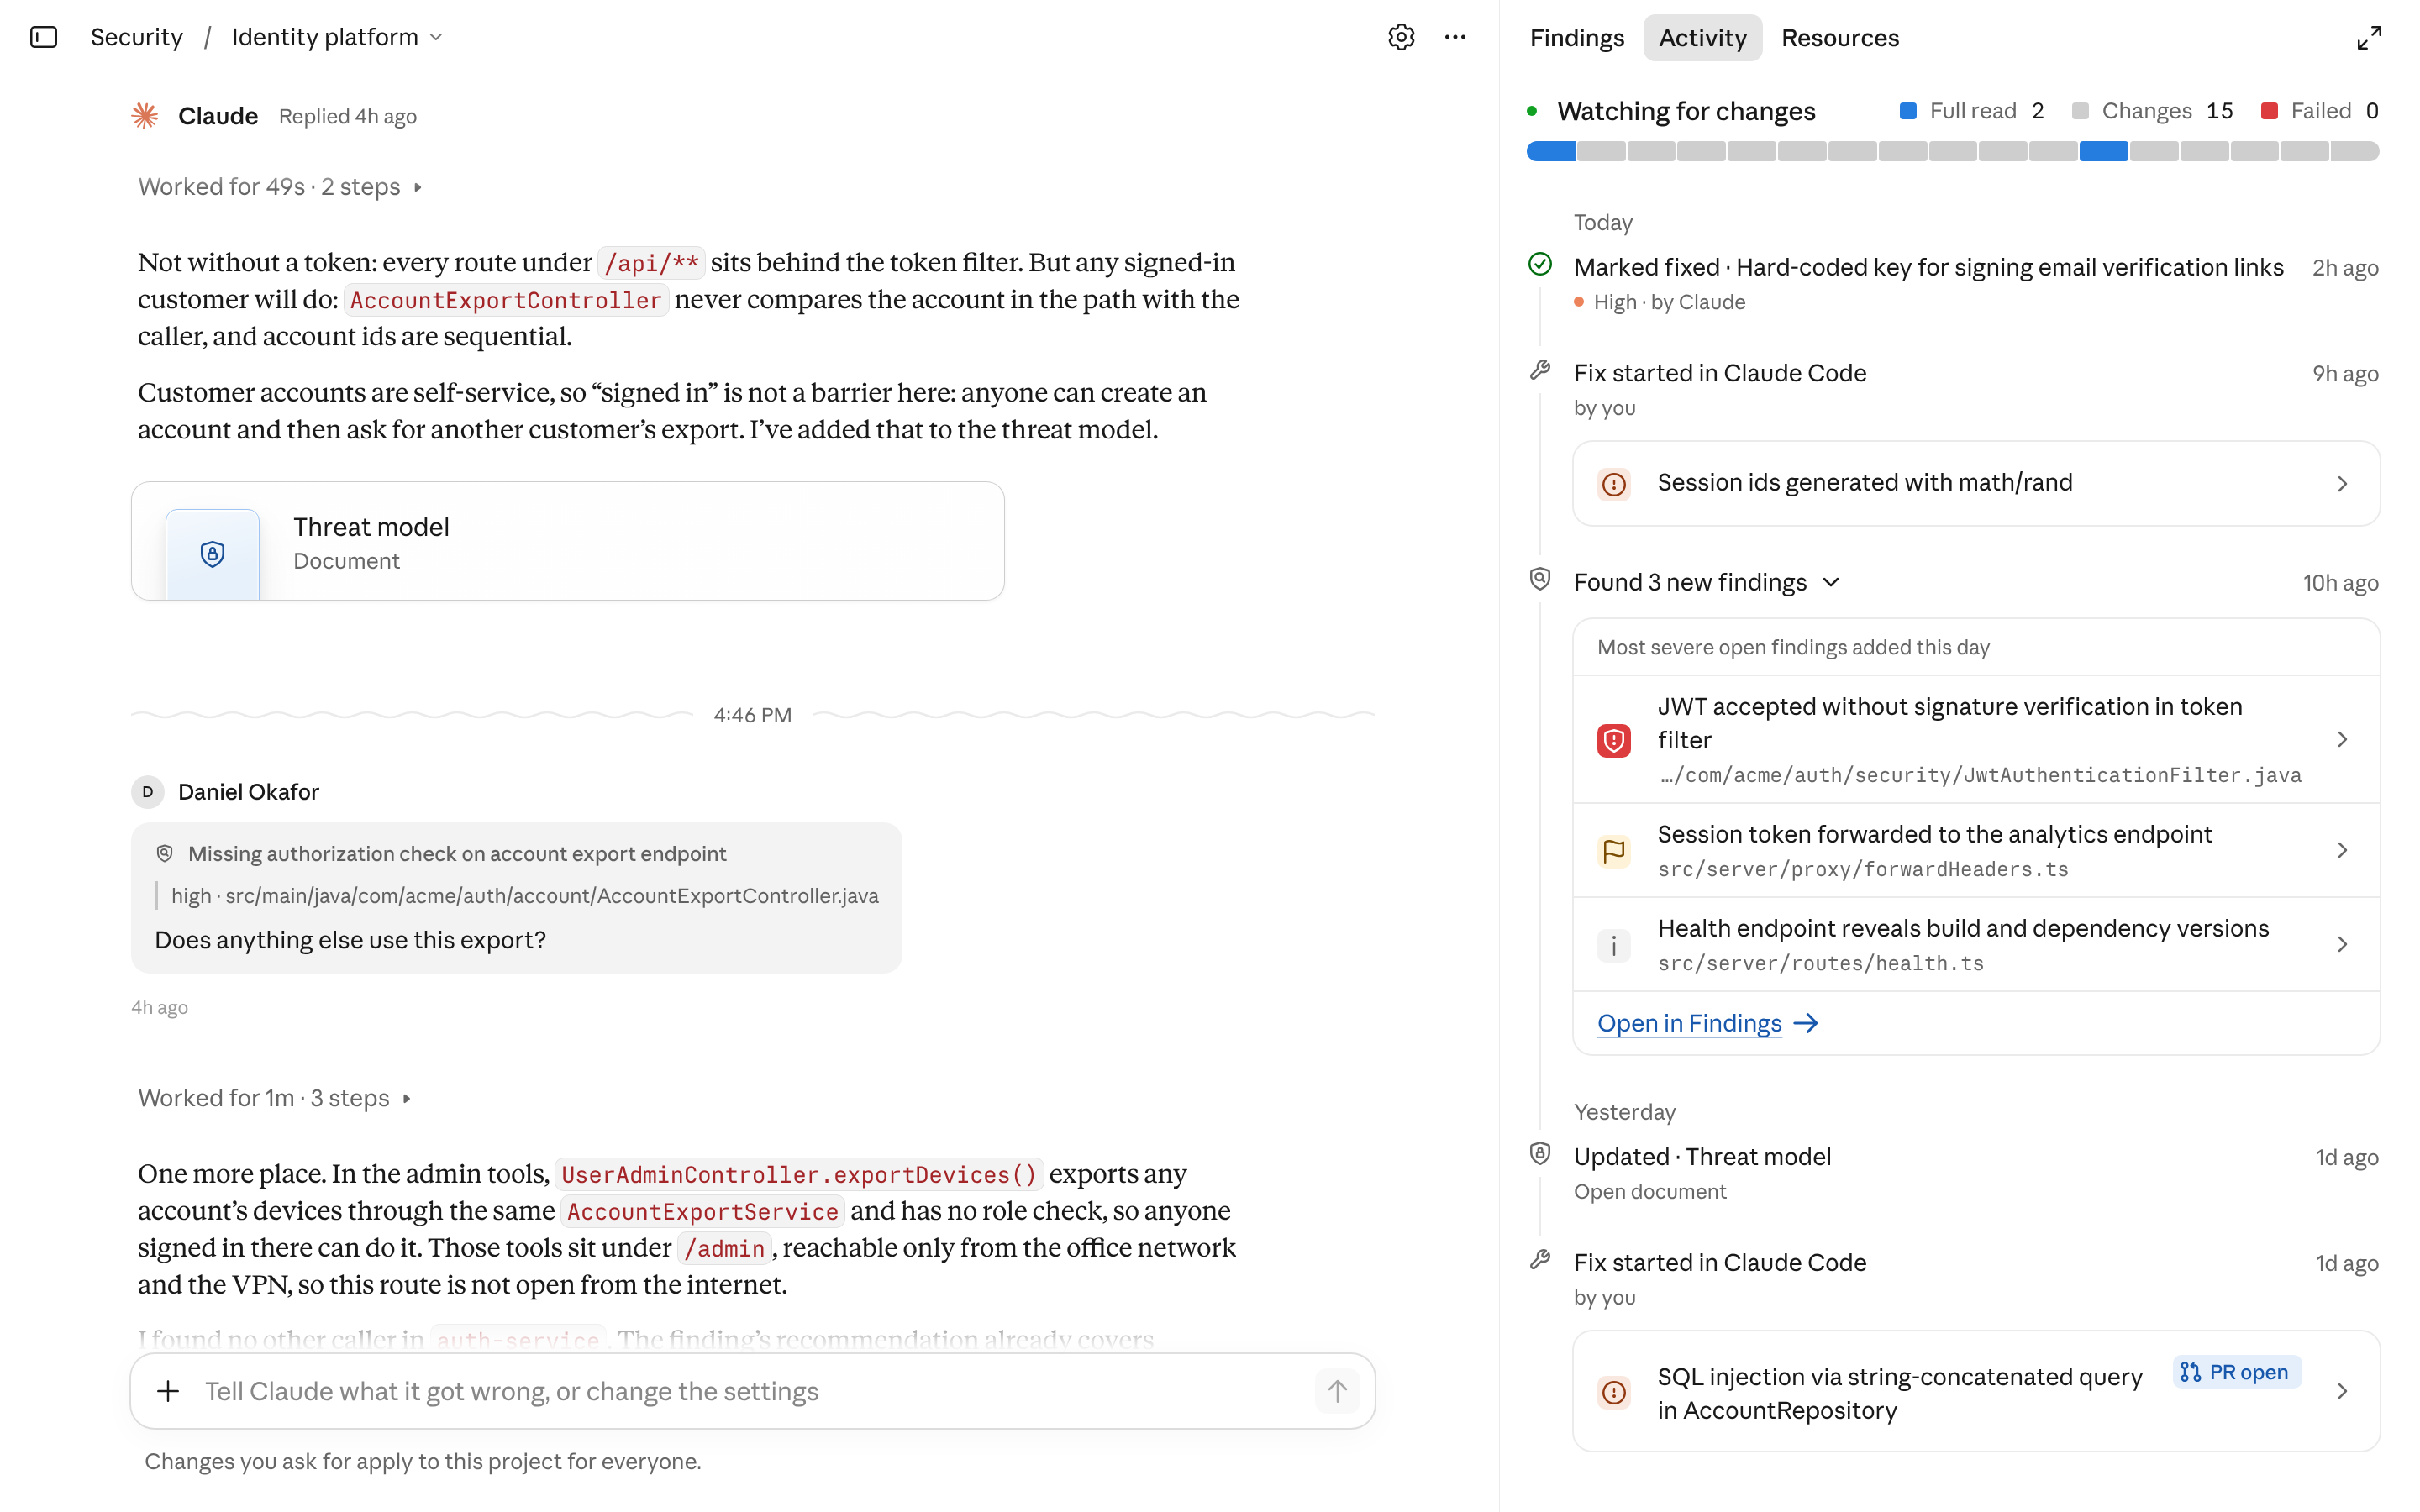
Each project also includes a knowledge base where teams can describe deployment practices, security policies, and controls that source code alone can't identify. Claude Security generates an editable threat model from the code, then uses that model and the added context to assess later scans. Every finding receives a severity rating and an explanation of how an attacker could reach the vulnerable code, with some findings also providing an attack-path diagram.
The new API supports listing and reading projects and findings, resolving or reopening findings, and managing projects and repositories. Personal access tokens carry users' permissions, while webhooks can alert connected systems to new findings. An MCP connector for Claude and Claude Code lets engineers retrieve a finding, discuss it, begin a fix, and mark it resolved within one session. Role-based controls separately govern project viewing, triage, and project creation.
Since entering public beta in April, thousands of organizations have used Claude Security to identify more than one million vulnerabilities. It runs on the full Claude model family, including Claude Mythos, without requiring Cyber Verification Program access. Enterprise admins can enable the service from the admin console. Organizations receive $25,000 in free monthly usage credits for two months, with the offer applying to usage through December 31, 2026.
Related context
- Claude Security setup and continuous monitoring guide: Supports: Anthropic's guide now confirms continuous scanning, automatic fix tracking, and API/MCP access, and details the Enterprise setup requirements.


